Using Strings For Incident Investigation?

What is Strings?

Strings is a tool which is used to extract string (Text) from a program or any other file. By default it extracts a string having a minimum of 4 charterers (but this can be changed by using the -n switch).

How does the Strings work?

Strings can be helpful to find out any text (such as url’s). Even though Strings is a really helpful tool but can not be completely relied upon. you can not rely on Strings solely because the attacker also knows that you might use Strings therefore can plant false flags in the program to confuse or derail you from your analysis.

How does the Strings work?

  1. Open CMD/Powershell (from Windows) or Terminal (*NIX)
  2. Go to the directory where you have saved the Strings program (Downloads in this case)
  3. Use Strings
    • Syntax: ./strings.exe

Examples:

  1. Here we have used strings on the strings software itself.

2. Here we have used strings on the Eula.txt file.

Using Regshot For Incident Investigation?

What is Regshot?

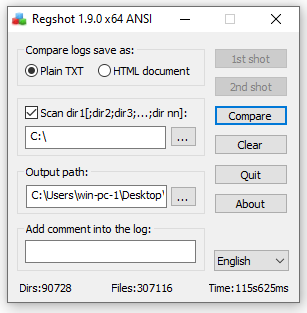
Regshot is a tool typically used for dynamic malware analysis. Even though the tool is typically used to analyse the malware changes but it can be used to track any changes made in the file system and the registry.

How does the Regshot work?

  1. We choose the result file format (In this case: plain txt file)
  2. check the scan directory check mark (In this case the whole ‘C:/’ drive)
  3. Choose the output location for the file (In this case the Desktop)
  4. Add any comments you would like to be in the logs (None in this case)
  5. Click on the 1st shot & choose shot or shot & save (I did a shot)
  6. Install the software or make any change you want (I installed VS code)

6. When you see the 2nd shot button click it and choose shot or shot & save (I did a shot)

7. Click compare, it will open the notepad file and then you can find all the changed in that notepad file.

Using Tasklist For Incident Investigation?

What is Tasklist?

Tasklist is a command-line tool that displays a list of currently running processes on the computer.


Common Commands:

tasklist

::: This command just shows the basic details about the running tasks. :::

tasklist /v

::: This command shows the active tasks with the verbose output about the verbose information. The following parameter and the meaning:

/v – Shows verbose task information :::

Click here to find some more parameters for Tasklist:

https://docs.microsoft.com/en-us/windows-server/administration/windows-commands/tasklist#parametersh

Using Netstat For Incident Investigation?

What is Netstat?

Netstat is a command-line network utility that displays network connections from a device.


Common Commands:

netstat

::: This command just shows the basic network connections :::

netstat -nao

::: This command shows the network connections with the process ID (PID) (Later we can track those PID to the image running using the tasklist command or on the Processes tab in Windows Task Manager). The following parameters and the meaning:

-n – no DNS resolves

-a – Displays all active TCP connections and the TCP and UDP ports

-o – This command shows the PID for each connection :::

netstat -naob

::: This command shows the network connections with the with the parent binary image that owns that process. The following parameters and the meaning:

-n – no DNS resolves

-a – Displays all active TCP connections and the TCP and UDP ports

-o – This command shows the PID for each connection

-b – This command shows the parent binary image that owns that process :::

Click here to find some more parameters for Netstat:

https://en.wikipedia.org/wiki/Netstat#Parameters